
Join the Conversation
- Find Answers
- :
- Splunk Administration
- :
- Admin Other
- :
- Knowledge Management
- :
- Knowledge bundle size issues
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Knowledge bundle size issues

Hi All,
I have this error message on the SH in Splunk:
{
Knowledge bundle size=3525MB exceeds max limit=2048MB. Distributed searches are running against an outdated knowledge bundle. Please remove/disable files from knowledge bundle or increase maxBundleSize in distsearch.conf.
}
What I did is increase the maxBundleSize in distsearch.conf :
I did this command on the server:
/opt/splunk/bin/splunk btool distsearch list --debug | grep maxBundleSize
and the result is:
/opt/splunk/etc/system/default/distsearch.conf maxBundleSize = 2048
So inside the /opt/splunk/etc/system/local/distsearch.conf I added the:
[replicationSettings]
maxBundleSize = 4000
Restarted Splunk, and noticed that the first error message is gone, but a new Yellow warning appeared:
{
The current bundle directory contains a large lookup file that might cause bundle replication fail. The path to the directory is /opt/splunk/var/run/InvestBank-SH-1-1681121119-1681121612.delta.
}
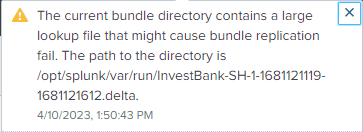
So I went to this path to check what is going on there:
cd /opt/splunk/var/run
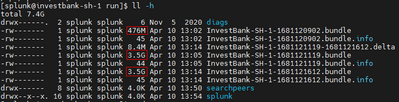
I have found 2 large files and one medium.
Can someone please advise me on what to do past this point?
I have found someone posted to check the below search:
index =_internal sourcetype=splunkd component=Archiver Archiving large_file=*
| stats count latest(size_in_bytes) by large_file

I don't know if this has any relation to the subject.
Please note that my Splunk environment is not a cluster.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


Look inside the large bundle files (they're just tarballs) to see what's making them so large. It's probably one or more huge lookup files. Make sure the lookups are expected to be that big as it's possible a bad search is appending rather than replacing data in the lookup.
If the lookup needs to be that large then remove it from the replication bundle ([repicationDenyList] in distsearch.conf) and distribute it to the indexers via another method.
If this reply helps you, Karma would be appreciated.

Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Accelerate Splunk App Development with AI
Splunk Agent Observability: Measuring AI Value with Splunk Tokenomics on AWS
Enterprise Security Watch Party: What’s New in 8.8 - Recap
