
Join the Conversation
- Find Answers
- :
- Splunk Administration
- :
- Admin Other
- :
- Knowledge Management
- :
- Field extraction using delimiter
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Field extraction using delimiter

I am having Structure data files for which I did field extraction using Splunk field delimiter in development box. when I packaged the app and placed it in production it is not working.
I checked the permission and it is global.
data looks like this
file name windows_patch.log
Step_Execution_Time~^~Applications~^~Server~^~Step_Name~^~Step_Status~^~Step_Logs~^~Step_Comment
13-01-2021 12:09:39 PM~^~SAP,SQL,Oracle~^~test2k19.testmbs.com~^~Connect to WSUS~^~Success~^~WinRM service is already running on this machine.\r\nWinRM is already set up for remote management on this computer.\r\n~^~ Connected to WSUS cidsuswuraeuw02.testmbs.com successfully.
13-01-2021 12:09:41 PM~^~SAP,SQL,Oracle~^~test2k19.testmbs.com~^~Loading PowerShell Modules on Target Host~^~Success~^~\nPowershell Output:\n~^~Fetch patches details successfully to apply on Target Hosttest2k19.testmbs.com.
Props.conf
[Windows_Pre_Patching]
REPORT-Patch-Windows_Pre_Patching = REPORT-Patch-Windows_Pre_Patching
transforms.conf
[REPORT-Patch-Windows_Pre_Patching]
DELIMS = "~^~"
FIELDS = "Step_Execution_Time","field2","field3","Applications","field5","field6","Server","field8","field9","Step_Name","field11","field12","Step_Status","field14","field15","Step_Logs","field17","field18","Step_Comment","Step_Comment"
please guide
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

Hi @ChetanArgekar ,
If it is working in a test environment then it should work in production as well.
Run a btool command and see what is the issue
And also check the local. meta for that app.
And also how are you checking the extractions? Are you running the search in fast mode?
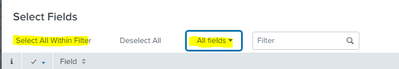
Run a search in verbose mode and see. And make sure you have selected the All fields.


Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
SOC4Kafka - New Kafka Connector Powered by OpenTelemetry
Rounding off the Splunk Dashboard Contest
A Four Part Event Series: AI + Observability: AI Agents, LLMs, Apps, & Infrastructure
