
Join the Conversation
- Find Answers
- :
- Splunk Administration
- :
- Getting Data In
- :
- Re: Is it possible to dump / drop data that is cur...
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Is it possible to dump / drop data that is currently in queue?

Production had a bug. One of the results of that bug was massive "over logging" of production nodes and those logs were forwarded (universal forwarder) to our splunk server.
Development reverted production, but Splunk was "log-jammed" as indicated by the queues for several hours:
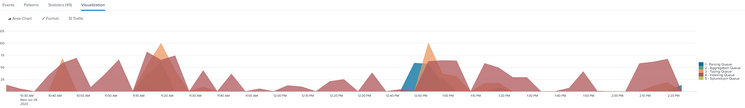
We know that we can clear the backlog on the clients (splunk universal forwarders) by turning off the forwarder, cleaning out the application logs as well as the following forwarder files:
\<application logs>
\var\log\splunk\metric*
\var\lib\splunk\fishbucket*
<restart forwarder>
It seems that several of the forwarders successfully forwarded data, so this jammed up our queues. I realize that Splunk is designed NOT to lose data, but assuming we were willing to accept some "pending" data loss, is there any way to clear the server side queues or "dump data" from indexing to clear a backlog?
We considered "blacklisting" specific files from indexing as was done in this post, but as indicated by the post, removing un-doing the blacklist results in those files going back for index processing.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


r. Ismo


Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Supercharging Windows Security Detection Performance: Introducing Hybrid Field ...
Enriching Signals with the OTel Lookup Processor
Meet the .conf26 AI Agent Buildathon Winners
