
Join the Conversation
- Find Answers
- :
- Splunk Administration
- :
- Getting Data In
- :
- Re: How to execute a py or sh by interface of Splu...
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
How to execute a py or sh by interface of Splunk
Hello,
I write a xxx.sh in the /splunk/etc/apps/my_apps/bin and by the commande line
./xxx.sh
to execute the code.
Could I add a bouton or something else in the interface of my app in Splunk
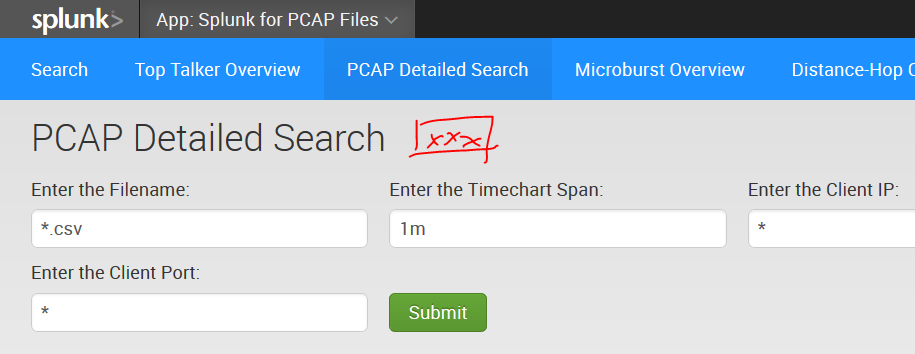
to trigger the xxx.sh.
Thank you very much
Hanzhi
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

http://answers.splunk.com/answers/25658/whats-the-point-of-custom-python-scripts.html
This is what I did
Put my custom python script in this folder
/var/sky/splunk/etc/system/bin
import csv
import sys
import splunk.Intersplunk
import string
(isgetinfo, sys.argv) = splunk.Intersplunk.isGetInfo(sys.argv)
if len(sys.argv) < 2:
splunk.Intersplunk.parseError("No arguments provided to custom script")
results = splunk.Intersplunk.readResults(None, None, True)
splunk.Intersplunk.outputResults(results)
Modify commands.conf file in below folder
/var/sky/splunk/etc/system/local
defaults for all external commands, exceptions are below in individual stanzas
type of script: 'python', 'perl'
TYPE = python
default FILENAME would be .py for python, .pl for perl and otherwise
is command streamable?
STREAMING = true
maximum data that can be passed to command (0 = no limit)
MAXINPUTS = 50000
end defaults
[customtest]
filename = customtest.py
To reload the setting run this URL in your browser (Just in case, if required)
https://SPLUNK_HOSTNAME:PORT/debug/refresh
And this is how we can use custom command in splunk
| customtest GETINFO [Inputparameters]

Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Persistent Queue at TcpOut — One of Splunk's Most Practical Features
Catalog Is Now Generally Available on Splunk Cloud Platform
Your Path to AgenticOps: AI Experiences for Every Splunk Practitioner
