
Join the Conversation
- Find Answers
- :
- Splunk Administration
- :
- Getting Data In
- :
- Filter records using time modifiers
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Filter records using time modifiers

Can someone tell me why this is not working:-
I need to filter records having 'Start_Time' within the mentioned range:
Working:-
index=imt_mobile source="*LTS_Validation_1" |eval early=relative_time(now(),"-3w@w")|eval late=relative_time(now(),"-2w@w")| where Start_Time<late|table "Track" "CO" early Start_Time late|
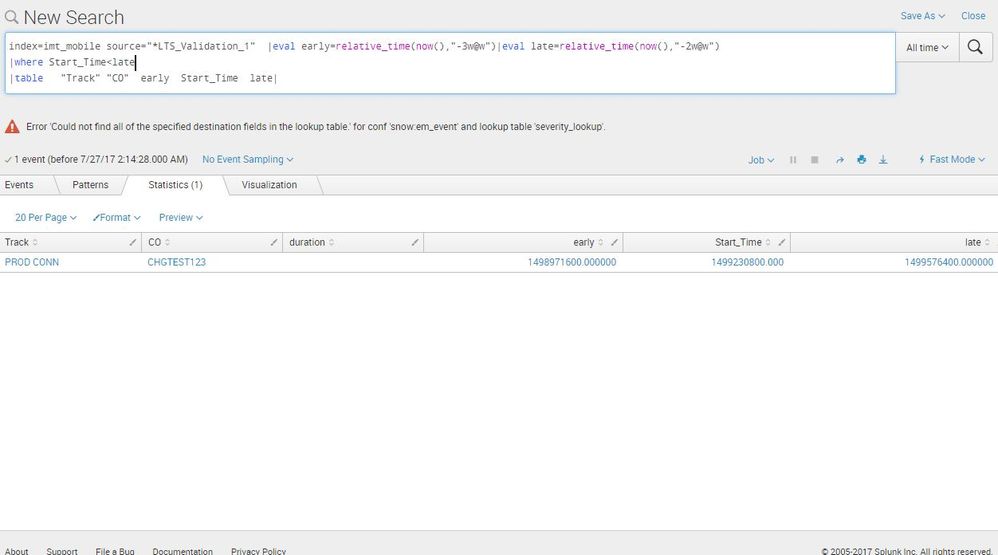
Here Start_Time was before 'late' so coming fine.
Not Working:-
index=imt_mobile source="*LTS_Validation_1" |eval early=relative_time(now(),"-3w@w")|eval late=relative_time(now(),"-2w@w")| where Start_Time<"-2w@w"|table "Track" "CO" early Start_Time late|
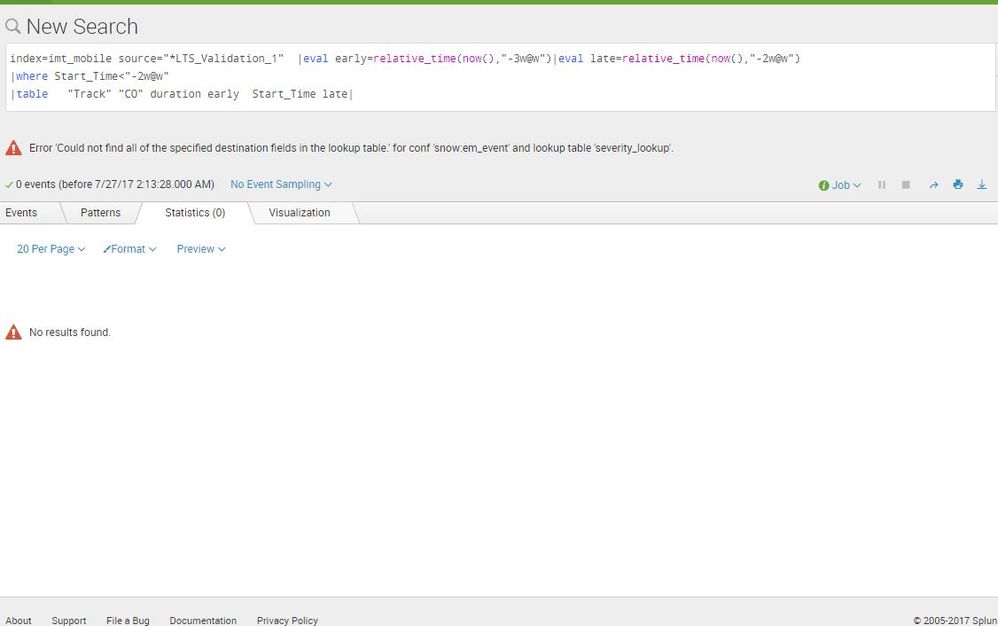
Here it is not working!!


- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


Hi dsiob,
sorry but I don't understand your problem:
in a where condition you have to compare two similar fields: if you use " -2w@w " Splunk don't understand that you're speaking about a time in epochtime format, so you need to transform "-2w@w" in epochtime format to compare with StartTime.
To do this you have to use (as in your first example) |eval late=relative_time(now(),"-2w@w")| where Start_Time<late
So, what is the problem to use eval?
If instead you need to show in Human readable format the three dates use strftime command:
| eval early=strftime(early,"%d/m/%Y %H.%M.%S"), late=strftime(late,"%d/m/%Y %H.%M.%S"), StartTime=strftime(StartTime,"%d/m/%Y %H.%M.%S")
Bye.
Giuseppe
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
so in place of "-2w@w" I need to use $mytime.Latest$, If I go with eval late=strftime(late,"%d/m/%Y %H.%M.%S") then It does not work If value of $mytime.Latest$ is "now". It is not able to convert "now" to epochtime
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Now() is already in epochtime.
you can see with
index=_internal | head 1 | eval late=now() | table late
beware that in your eval command you losed one %.
Bye.
Giuseppe

Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Splunk Enterprise Security: An Automated Phishing Response Workflow
Sharper ES Detections, Agentic AI Integrations, Smarter Workload Management, and More ...
Data Outage Monitoring and Reporting
