
Join the Conversation
- Find Answers
- :
- Splunk Administration
- :
- Getting Data In
- :
- Re: Custom timestamps for csv format?
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
I have the following data from csv file that I want to index into splunk.

I want to set the timestamp to be the highlighted portions but if I select auto for timestamp it will grab the first timestamp that it detects. So I modify the props.conf file to add the following line:
TIME_PREFIX=^([^,]*,){4}
which tell it to take the timestamp after the 4th comma. But for some reasons it grabs the 10-27-2017 along with 00:04:44 but skip the 6:20 PM (which is the actual time that i need). Is there anything I could do to avoid this? Thanks!
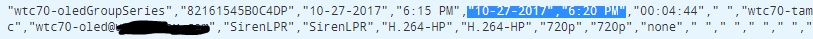
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


So, it looks like its grabbing the correct field.
Have you provided a TIME_FORMAT?
Splunk can't recognize on its own that 00:04:44 is NOT the correct time. it is the most common sense thing to be the time.
So you need to provide the CORRECT FORMAT.
something like:
TIME_FORMAT="%m-%d-%Y","%I:%M %p"
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
work like a champ. thanks!
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
huzzah!!!!

Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
[Puzzles] Solve, Learn, Repeat: Classic British Rock Bands
New to the Community? Join Us for an Exclusive Post .conf26 Welcome Session (Plus a ...
Accelerate Splunk App Development with AI
