
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Dashboards & Visualizations
- :
- Re: Splunk graphs the future
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Splunk graphs the future

I'm running Splunk version: 4.2.3-105575
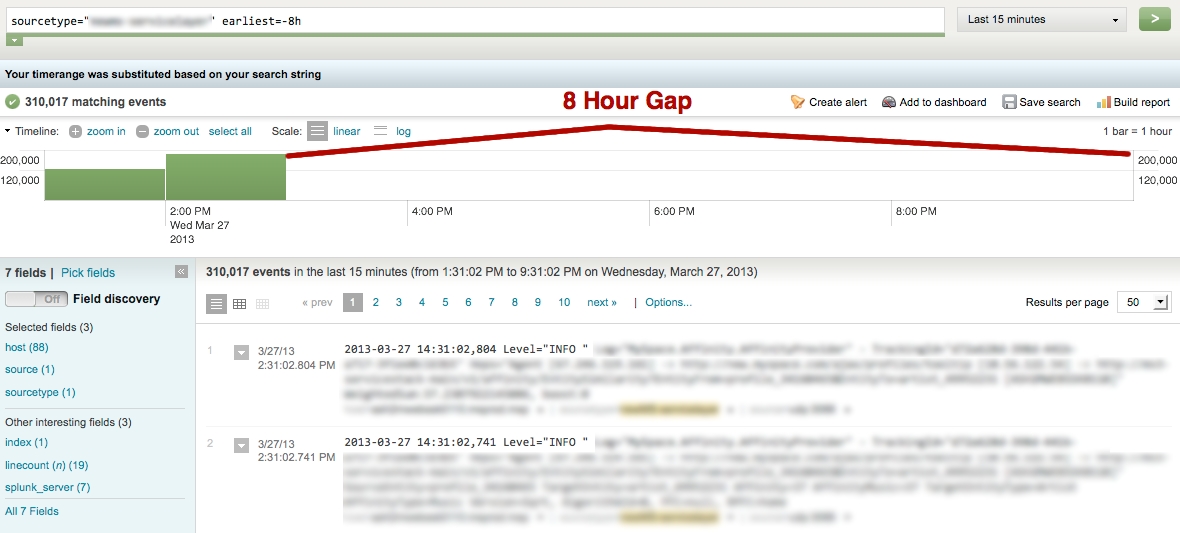
Searcher and indexers are all set to GMT which may be the cause. Looking at all the events of a particular sourcetype, the Index time, Source time, and even the bar graph Display time are all correct, but the bar graph believes there is 8 hours of data missing in the future. This is affect other graphs we build off and affects our analysis trending. http://www.ugu.com/splunk/gap8hr.jpg
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hello
Have you checked the timezone settings for your user?
Regards
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
All other primary splunk conf files (inputs, props, transforms, server, web, etc…) are the same between indexer0001 and indexer022. It also worth noting that the issue does not appear with "some" of the other sourcetypes on indexer022.
Could there be a hidden conf somewhere that has a stanza uniquely configured for this sourcetype (servicelog) and a few others. I haven't found anything in the normal config files.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Yes. Further investigating reveals.
All splunk servers are running Linux Centos 5.x, all have the same Splunk version: 4.2.3-105575
From the Searcher, the following exhibits the gap between PDT and UTC on our standard OS built indexers (as seen in the attached link above). This we know already know.
sourcetype="servicelog" earliest=-8h splunk_server="indexer022"
We have an indexer on an old non-standard OS that everything works fine and there is no gap.
Also worth noting that the issue does not appear with "some" of the other sourcetypes on indexer022.
An help is greatly appreciated...


Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Cisco Data Fabric from Architecture to Investigation, Better SOC Visibility, and More ...
The Trust Gap: Why a Data Foundation is Fundamental to an Agentic Enterprise
Data Management Digest – September 2026
