
Join the Conversation
- Find Answers
- :
- Apps & Add-ons
- :
- All Apps and Add-ons
- :
- All Apps and Add-ons
- :
- time range splunk search & increase time range
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
time range splunk search & increase time range

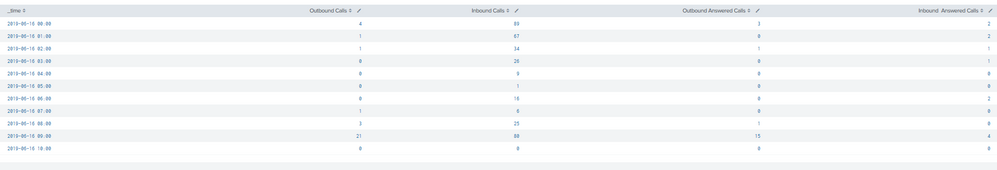
currently when I am running below query getting hourly count, but I need to have count always start from 00:00 to 01:00, 00:00 to 02:00, 00:00 to 03:00, 00:00 to 04:00, 00:00 to 05:00 ....... 00:00 to current hour.
How I can modify below query so that I will get output hourly but search clock always start from 00:00. It would be great if anyone can help me.
index=mdp_ivc_cdrs sourcetype=prd_mdp_ivc_cdrs earliest=@d latest=now | bucket _time span=1h |timechart span=1h count(eval(like(INGRESS_TRUNKCONTEXT,"%amazon%"))) as "Outound Calls",count(eval(like(INGRESS_TRUNKCONTEXT,"%vodafone%"))) as "Inbound Calls",count(eval(like(INGRESS_TRUNKCONTEXT,"%amazon%") AND CDR_TYPE=2 AND ANSWERED_CALL=1)) as "Outbound Answered Calls",count(eval(like(INGRESS_TRUNKCONTEXT,"%vodafone%") AND CDR_TYPE=2 AND ANSWERED_CALL=1)) as "Inbound Answered Calls"
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi @rups260386,
Since you're already counting hour by hour from earliest=@d then all you have to do is add this to the end of your search |streamstats sum(*) as *to make an incremental sum of the results.
Your search should then look like this :
index=mdp_ivc_cdrs sourcetype=prd_mdp_ivc_cdrs earliest=@d latest=now
| bucket _time span=1h
| timechart span=1h count(eval(like(INGRESS_TRUNKCONTEXT,"%amazon%"))) as "Outound Calls",count(eval(like(INGRESS_TRUNKCONTEXT,"%vodafone%"))) as "Inbound Calls",count(eval(like(INGRESS_TRUNKCONTEXT,"%amazon%") AND CDR_TYPE=2 AND ANSWERED_CALL=1)) as "Outbound Answered Calls",count(eval(like(INGRESS_TRUNKCONTEXT,"%vodafone%") AND CDR_TYPE=2 AND ANSWERED_CALL=1)) as "Inbound  Answered Calls"
|streamstats sum(*) as *
Cheers,
David
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
I am not sure I understand the question, as it seems your query already accomplishes this task.
earliest=@d
in your query, does what you are requesting
Please explain further
Edit:
Are you looking for a cumulative count?
Try this:
index=mdp_ivc_cdrs sourcetype=prd_mdp_ivc_cdrs earliest=@d latest=now
| bucket _time span=1h
| timechart span=1h count(eval(like(INGRESS_TRUNKCONTEXT,"%amazon%"))) as "Outound Calls",count(eval(like(INGRESS_TRUNKCONTEXT,"%vodafone%"))) as "Inbound Calls",count(eval(like(INGRESS_TRUNKCONTEXT,"%amazon%") AND CDR_TYPE=2 AND ANSWERED_CALL=1)) as "Outbound Answered Calls",count(eval(like(INGRESS_TRUNKCONTEXT,"%vodafone%") AND CDR_TYPE=2 AND ANSWERED_CALL=1)) as "Inbound  Answered Calls"
| streamstats sum("Outbound Calls") ,sum("Inbound Calls") , sum("Outbound Answered Calls") ,sum("Inbound  Answered Calls")



Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Thanks for the Memories: .conf26 Took Learning to New Heights
Best Practices: Splunk auto adjust pipeline queue
Splunk Auto Ingestion Parallel Pipeline Scaling
