
Join the Conversation
- Find Answers
- :
- Apps & Add-ons
- :
- All Apps and Add-ons
- :
- All Apps and Add-ons
- :
- Data input for Browsing History analysis app
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Data input for Browsing History analysis app
Hello,
I am new to Splunk and am trying to get the browsing histroy analysis app running on splunk eterprise (demo) that is capturing local logs as well as logs from a UF. I am stummped as I do not know what data input to use and there is not very much documentaion. That I have be able to find. Any help getting the data input setup would bre greatly appreciated.
Thanks
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
I Installed 6.5.10 and configured all windows event logs locally and see events coming in but nothing in the borwser index and nothing in the dashboar even after a restart.
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

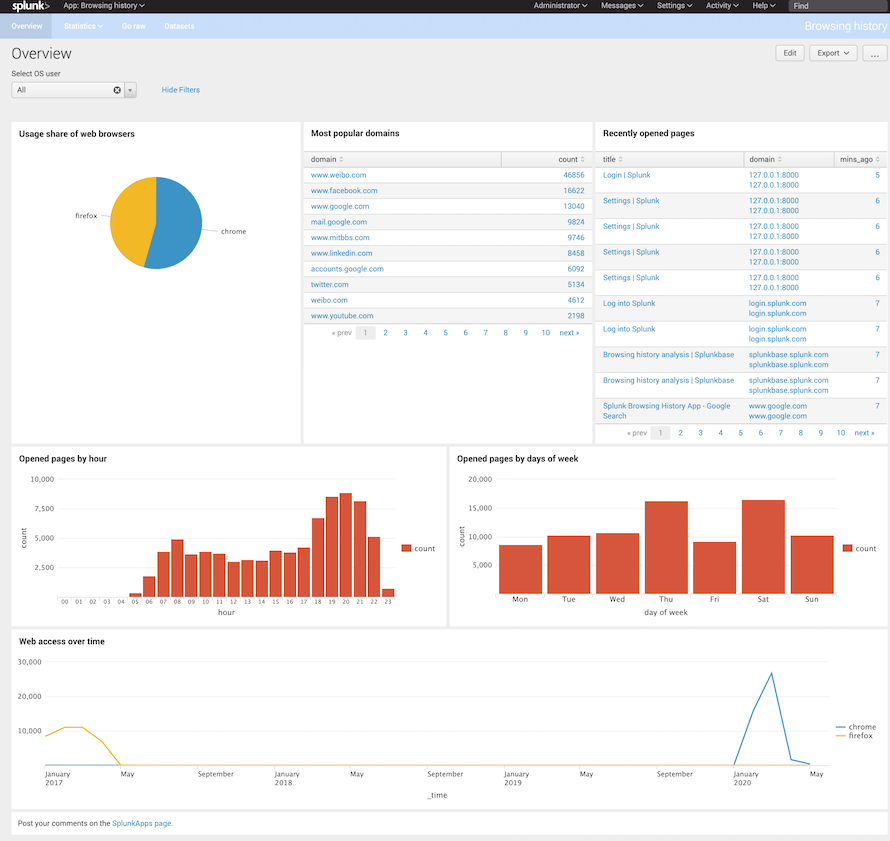
If you install the app on the search head and restart Splunk of a supported version, it should ingest the local data and show dashboards visualizing the data right away (see attached). Even though it says it only supports Splunk Versions: 6.5, 6.4, 6.3, 6.2, 6.1, 6.0, 5.0, you can get it running on 7.0 as well.
If you have a heavy forwarder, it is easy, just install the app and forward it to the right index, browser in this case. However, to get data in from a remote machine with UF is another ball game, as this app uses Python, you will have to install your own Python interpreter on the UF and tinker around to make it work.



Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Data Management Digest – September 2026
Federated Search for CloudWatch Unified Data Store Is Generally Available
Announcing Modern Navigation: A New Era of Splunk User Experience
