
Join the Conversation
- Find Answers
- :
- Apps & Add-ons
- :
- All Apps and Add-ons
- :
- All Apps and Add-ons
- :
- Access Virus Total permalink with Splunk
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

I am interested in developing an app where Virus total URL scan results will be displayed (rather than the permalink) in Splunk. To be more specific access the data in the Virus Total Permalink and in the permalink it says under "scans" "detected" if it is True output clean site else else Not clean.
I have generated the code for checking if "scans" "detected" is True/False. But I do not know how to access data in Virus total permalink through splunk
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

With "VirusTotal Malware Lookup for Splunk", this should be possible.
While in its default mode the | virustotal command outputs structured fields (columns), you can also run the command in "raw" mode - where all the output sent by VirusTotal is passed back to Splunk in json format. From there it should be possible to use | spath or a similar Splunk command to post-process the json and extract relevant fields.
Default usage:

Raw json output mode:
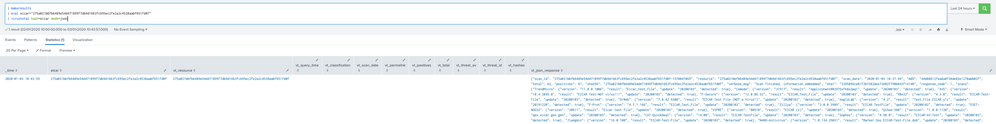
(please excuse the small images - it may be worth opening them in a different tab to better see content)
Unfortunately, any additional data that's not included in the json is currently not obtainable by the TA.
Hopefully this helps.
Please reach out with any further questions.
Thanks,
Tomasz
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
With "VirusTotal Malware Lookup for Splunk", this should be possible.
While in its default mode the | virustotal command outputs structured fields (columns), you can also run the command in "raw" mode - where all the output sent by VirusTotal is passed back to Splunk in json format. From there it should be possible to use | spath or a similar Splunk command to post-process the json and extract relevant fields.
Default usage:
Raw json output mode:
(please excuse the small images - it may be worth opening them in a different tab to better see content)
Unfortunately, any additional data that's not included in the json is currently not obtainable by the TA.
Hopefully this helps.
Please reach out with any further questions.
Thanks,
Tomasz




Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
A Four-Part Event Series: Full Stack Observability For the AI Era
SOC4Kafka - New Kafka Connector Powered by OpenTelemetry
Event Series: Level up your SOC: Advancing with Splunk Enterprise Security
