
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Splunk Search
- :
- which overrides first either time modifier or time...
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
which overrides first either time modifier or time range picker?

I have created Splunk query with time modifiers "earliest" and "latest" ( for eg. earliest="15/01/2022 8 am" latest="15/01/2022 10 pm" ) and also I have selected time range in the time ranger picker (for eg. 23/12/2022 8 am to 23/12/2022 10 pm)
Splunk Query:
timeformat="%m-%d-%Y %l:%M %p" earliest="15-01-2022 08:00 AM" latest="15-01-2022 10:00 PM" index="mobileApp" homepage
Time range picker values in UI:
From: 23/12/2022 8 am; To: 23/12/2022 10 pm
whenever, I click 'search' button, time range picker overrides the time modifiers earliest/latest values which are used in the Splunk query
Question:
could you please help me on overriding 'time range picker' values ( I need results between 15/01/2022 8 am to 15/01/2022 10 pm based on 'time modifiers' only)
Your answer would be greatly appreciated!
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


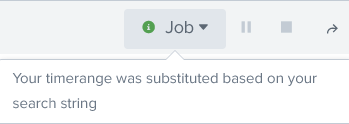
The times used for earliest and latest in your query should override the timepicker values. The job inspector should have a message saying this has happened


Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Event Series: Level up your SOC: Advancing with Splunk Enterprise Security
Announcing Modern Navigation: A New Era of Splunk User Experience
SOC4Kafka - New Kafka Connector Powered by OpenTelemetry
