
Join the Conversation
- Find Answers
- :
- Splunk Products
- :
- Splunk Enterprise
- :
- Why is Splunk forwarder is not active?
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Why is Splunk forwarder is not active?

Greetings!!
I'm getting the warning alerts showing me that splunk forwarder is not active, as shown on the below pic,
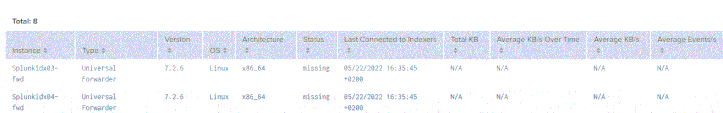
splunk forwarder is running (/opt/splunkforwarder/bin/splunk status
) but in Monitoring Console under Forwader:Management is not active it's showing a missing status,as shown on the above screenshot
even when I try to stop and restart the splunkforwader service(/opt/splunkforwarder/bin/splunk stop) can't be stopped, as shown on the below screenshot
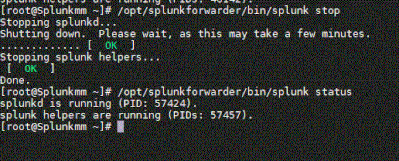
Kindly help me on how i can fix the error,
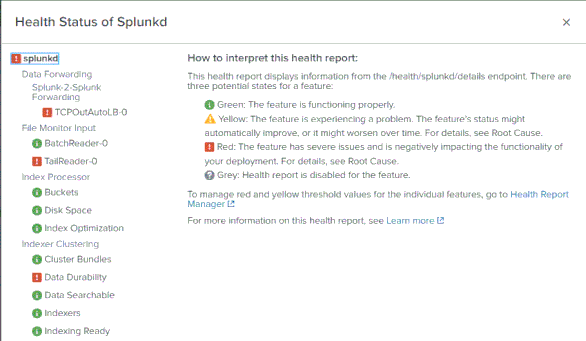
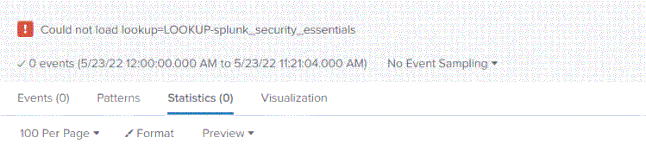
Another error while searching:( I am running splunk_security_essentials version 3.0.0.)
***********************************
error 1:
Could not load lookup=LOOKUP-splunk_security_essentials
error2:
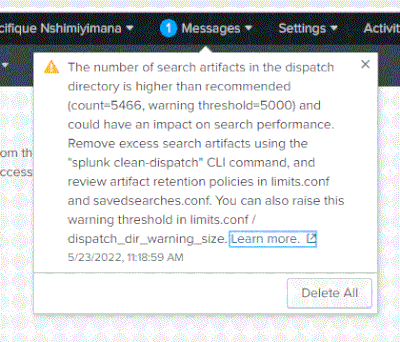
How about and root cause of this error2 above? and how to fix this?
Also find the this Warning error, I got from splunkd.log
05-22-2022 19:54:02.957 +0200 WARN SSLCommon - Received fatal SSL3 alert. ssl_state='SSLv3 read server certificate B', alert_description='certificate expired'.
05-22-2022 19:54:02.957 +0200 ERROR TcpOutputFd - Connection to host=x.x.x.17:9997 failed. sock_error = 0. SSL Error = error:14090086:SSL routines:ssl3_get_server_certificate:certificate verify failed - please check the output of the `openssl verify` command for the certificates involved; note that if certificate verification is enabled (requireClientCert or sslVerifyServerCert set to "true"), the CA certificate and the server certificate should not have the same Common Name.
05-22-2022 19:54:02.960 +0200 ERROR X509Verify - X509 certificate (O=SplunkUser,CN=SplunkServerDefaultCert) failed validation; error=10, reason="certificate has expired"
05-22-2022 19:54:02.960 +0200 WARN SSLCommon - Received fatal SSL3 alert. ssl_state='SSLv3 read server certificate B', alert_description='certificate expired'.
05-22-2022 19:54:02.960 +0200 ERROR TcpOutputFd - Connection to host=x.x.x.16:9997 failed. sock_error = 0. SSL Error = error:14090086:SSL routines:ssl3_get_server_certificate:certificate verify failed - please check the output of the `openssl verify` command for the certificates involved; note that if certificate verification is enabled (requireClientCert or sslVerifyServerCert set to "true"), the CA certificate and the server certificate should not have the same Common Name.
05-22-2022 19:54:02.964 +0200 ERROR X509Verify - X509 certificate (O=SplunkUser,CN=SplunkServerDefaultCert) failed validation; error=10, reason="certificate has expired"
05-22-2022 19:54:02.964 +0200 WARN SSLCommon - Received fatal SSL3 alert. ssl_state='SSLv3 read server certificate B', alert_description='certificate expired'.
05-22-2022 19:54:02.964 +0200 ERROR TcpOutputFd - Connection to host=x.x.x.14:9997 failed. sock_error = 0. SSL Error = error:14090086:SSL routines:ssl3_get_server_certificate:certificate verify failed - please check the output of the `openssl verify` command for the certificates involved; note that if certificate verification is enabled (requireClientCert or sslVerifyServerCert set to "true"), the CA certificate and the server certificate should not have the same Common Name.
Kindly help and guide me on how to fix this,
Thank you in advance.


Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Thanks for the Memories: .conf26 Took Learning to New Heights
Best Practices: Splunk auto adjust pipeline queue
Splunk Auto Ingestion Parallel Pipeline Scaling
