
Join the Conversation
- Find Answers
- :
- Splunk Administration
- :
- Admin Other
- :
- Knowledge Management
- :
- How to search sum rows by column?
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
How to search sum rows by column?
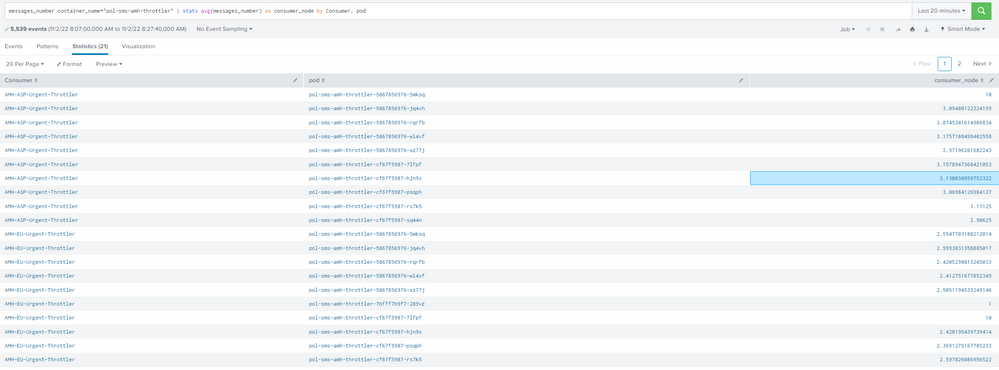
Having this initial query I obtain a list of results order by Consumer, and pod
messages_number container_name="pol-sms-amh-throttler" | stats avg(messages_number) as consumer_node by Consumer, pod
Then I append a second stats where I want to sum all the values of pods by Consumer
messages_number container_name="pol-sms-amh-throttler" | stats avg(messages_number) as consumer_node by Consumer, pod | stats sum(consumer_node) as AvgConsumption by Consumer limit=0
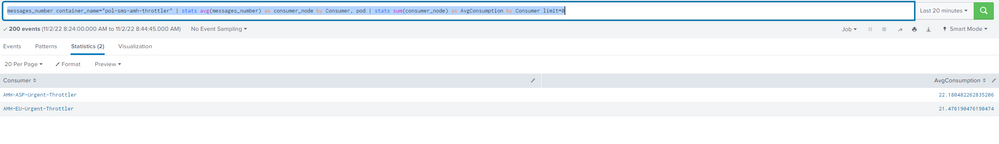
Is this query correct and accurate about what I'm want to achieve?
Also I don't know how can I see the AvgConsumptions in a visualization
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
you're not doing the same thing.
If we have 3 pods that are producing messages_number 3,4,2. What I want to know is that all of them are producing 9.
But with your query it will produce just 4
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


If you just want to sum them, try this
messages_number container_name="pol-sms-amh-throttler" | stats sum(messages_number) as TotalConsumption by Consumer limit=0- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
What you have will give you a number although I am not sure what significance it has - have you considered just doing it this way?
messages_number container_name="pol-sms-amh-throttler" | stats avg(messages_number) as AvgConsumption by Consumer limit=0

Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Thanks for the Memories: .conf26 Took Learning to New Heights
Best Practices: Splunk auto adjust pipeline queue
Splunk Auto Ingestion Parallel Pipeline Scaling
