
Join the Conversation
- Find Answers
- :
- Splunk Administration
- :
- Admin Other
- :
- Installation
- :
- Reinstalled Splunk after web interface went down, ...
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Reinstalled Splunk after web interface went down, still doesn't work

I recently had access to my Splunk web interface with morning. It said an update was required so I did that and then restarted Splunk. After the restart, the web interface never came back, Splunk would say it was running with ./splunk status command, and it was even listening on ports 8089 and 9997, which had been configured earlier. I tried everything to get it to work again and it just would not. My computers firewall was completely disabled and Splunk would continue to have an inactive web interface. I completely uninstalled it and reinstalled Splunk, and to my surprise:
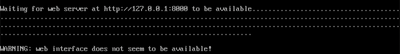
This frustrating message appeared. SO it seems I will no longer have access to the web interface even after a complete reinstall. Is this just a broken application now? Wouldn't a reinstall have gotten my Splunk back online when it worked only this morning?
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Make Your Machine Data AI-Ready in Splunk
Splunk Asynchronous Forwarding Explained
How to Monitor AI Agents with Splunk Agent Observability
