
Join the Conversation
- Find Answers
- :
- Splunk Administration
- :
- Getting Data In
- :
- Parsing XML log files
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Parsing XML log files

Hi,
I would to like to index a log in xml format and I would to like to parse it so that the content of each event was what was inside the tags, as shown below:
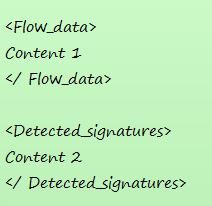
Event1 = content 1
Event2 = content 2
How can I do this? Is there a regular expression for the above example?
Best regards,
Lopes.

- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

@monteirolopes... depends on how you are loading XML data. Is the entire content itself XML or is XML part of content with some additional text without XML format.
For raw XML event
Based on whether you want to have Splunk perform automatic XML extraction during index time or search time you can choose between either one of INDEXED_EXTRACTIONS or KV_MODE as XML. Refer to the following documentation: http://docs.splunk.com/Documentation/Splunk/latest/Data/Extractfieldsfromfileswithstructureddata#Pro...
For XML data as a subset of raw event
You can use spath to traverse XML once you have extracted XML Data.
Please find below run anywhere search for your mock data. Also refer to spath documentation: http://docs.splunk.com/Documentation/Splunk/latest/SearchReference/Spath
| makeresults
| eval mockXMLData="<Flow_data>Content1</Flow_data><Detected_signatures>Content2</Detected_signatures>"
| spath input=mockXMLData path=Detected_signatures output=key
| table key mockXMLData
PS: You can apply regular expression using rex, command but spath has been written specifically for XML and JSON data parsing.
| makeresults | eval message= "Happy Splunking!!!"

Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
[Puzzles] Solve, Learn, Repeat: Classic British Rock Bands
New to the Community? Join Us for an Exclusive Post .conf26 Welcome Session (Plus a ...
Accelerate Splunk App Development with AI
