
Join the Conversation
- Find Answers
- :
- Apps & Add-ons
- :
- All Apps and Add-ons
- :
- All Apps and Add-ons
- :
- Issue with Splunk Infrastructure Monitoring Add-On...
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Issue with Splunk Infrastructure Monitoring Add-On: SSL: TLSV1_ALERT_INTERNAL_ERROR

I configured the Splunk Infrastructure Monitoring add-on with Splunk Observability Cloud in order to receive infrastructure metrics from Splunk Observability. The connection was successful, as confirmed by the Add-On's Connection Status test:

However, when I try to search for any data using the sim flow command, I receive the following error:
Error in "sim" command: Error executing SignalFlow program. error_msg=[SSL: TLSV1_ALERT_INTERNAL_ERROR] tlsv1 alert internal error (_ssl.c:1106)".

| sim flow query="data('cpu.utilization', filter=filter('host', '*') and (not filter('cloud.provider', '*')) and (not filter('AWSUniqueId', '*')) and (not filter('gcp_id', '*')) and (not filter('azure_resource_id', '*')) and (not filter('kubernetes_node', '*')), extrapolation='last_value', maxExtrapolations=2).mean(by=['host']).count().publish()"
I have done this kind of configuration several times, but I have never incurred in such an error. I even used the same query on another configuration to cross-check, and it's working fine.
Could it be a connection issue? Perhaps the search head is blocking some outside connection? Or is my environment using a different SSL package? Nevertheless, something seems to be preventing data from coming in.
Additionally sharing type+version of the OS instance:

And OpenSSL version:
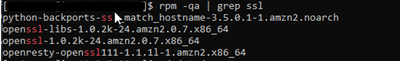
Does anyone have any suggestions, tips, ideas?
Thanks!


Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
A Four-Part Event Series: Full Stack Observability For the AI Era
SOC4Kafka - New Kafka Connector Powered by OpenTelemetry
Event Series: Level up your SOC: Advancing with Splunk Enterprise Security
