
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Splunk Search
- :
- "Q" Encoding
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hello,
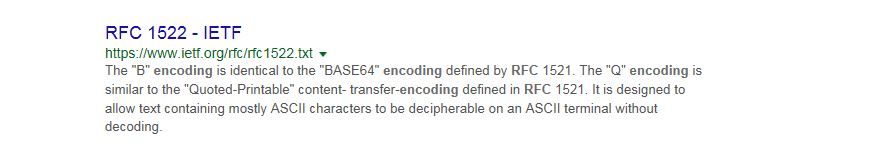
I have a field which contains values encoded in "Q" (I just discovered this encoding type : RFC 1522). It seems to be used a lot in email logs.
I wasn't able to find any commands that helps to convert to a 'readable' string.
Any help, idea, suggestion would be appreciated in order to convert these values (by Splunk commands or by fields extractions processs).
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

Hi,
I took a little stupid test message "Why is a Q encoded string (random text <>)?", tried an online Q encoder to encode this to "Why_is_a_Q_encoded_string_=28random_text_=3C=3E=29=3F" and could decode this in Splunk with 2 rex commands:
| makeresults | eval input="Why_is_a_Q_encoded_string_=28random_text_=3C=3E=29=3F" | rex field=input mode=sed "s/=(..)/%\1/g" | rex field=input mode=sed "s/_/ /g" | eval output=urldecode(input)
Not sure if this covers the whole spec, test it out with your real data.
Hth,
-Kai.
edit: actually, this looks much nicer:
| makeresults | eval input="Why_is_a_Q_encoded_string_=28random_text_=3C=3E=29=3F" | eval output=urldecode(replace(replace(input,"=","%"),"_","%20"))
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Can you please give us an example of these "Q" values? maybe a snapshot...
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi,
I took a little stupid test message "Why is a Q encoded string (random text <>)?", tried an online Q encoder to encode this to "Why_is_a_Q_encoded_string_=28random_text_=3C=3E=29=3F" and could decode this in Splunk with 2 rex commands:
| makeresults | eval input="Why_is_a_Q_encoded_string_=28random_text_=3C=3E=29=3F" | rex field=input mode=sed "s/=(..)/%\1/g" | rex field=input mode=sed "s/_/ /g" | eval output=urldecode(input)
Not sure if this covers the whole spec, test it out with your real data.
Hth,
-Kai.
edit: actually, this looks much nicer:
| makeresults | eval input="Why_is_a_Q_encoded_string_=28random_text_=3C=3E=29=3F" | eval output=urldecode(replace(replace(input,"=","%"),"_","%20"))
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Perfect, exactly what I'm looking for :). Indeed use urldecode is much easier.



Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
Supercharging Windows Security Detection Performance: Introducing Hybrid Field ...
Ditch the Manual Grind: Building AI Agents with Splunk
Cisco Data Fabric from Architecture to Investigation, Better SOC Visibility, and More ...
