
Join the Conversation
- Find Answers
- :
- Using Splunk
- :
- Splunk Search
- :
- Reading from a specific log file
- Subscribe to RSS Feed
- Mark Topic as New
- Mark Topic as Read
- Float this Topic for Current User
- Bookmark Topic
- Subscribe to Topic
- Mute Topic
- Printer Friendly Page
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content

Hi, I am very new to Splunk. I would like to know how to search just the latest log file from the below screenshot. (i.e. the current days file only)
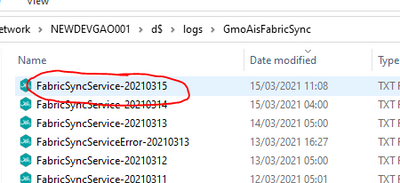
At the moment I have the below search query , but this is pulling all the files so I'm just not sure how of the syntax for adding the current days date string. Ultimately I am looking to find errors real time which send an alert.
source="d:\\logs\\gmoaisfabricsync\\fabricsyncservice-*.txt"
Cheers,
Rob
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content


Hi @rsmall13,
if every file contains only events of a specific day, you could use your search restricting the time period of your search (e.g. today, or yesterday or the last 24 hours).
Only one hint: use always the index condition to have faster searches.
Ciao.
Giuseppe
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Ok thanks, that should work! I am also using an index as well.
index="test_apps" AND sourcetype="gao" source="D:\\logs\\GmoAisFabricSync\\FabricSyncService-*.txt"
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
- Mark as New
- Bookmark Message
- Subscribe to Message
- Mute Message
- Subscribe to RSS Feed
- Permalink
- Report Inappropriate Content
Hi @rsmall13,
if every file contains only events of a specific day, you could use your search restricting the time period of your search (e.g. today, or yesterday or the last 24 hours).
Only one hint: use always the index condition to have faster searches.
Ciao.
Giuseppe


Join the Splunk Community Slack to learn, troubleshoot, and make connections with fellow Splunk practitioners in real time!
Join Splunk User Groups to connect and learn in-person by region or remotely by topic or industry.
SOC4Kafka - New Kafka Connector Powered by OpenTelemetry
Rounding off the Splunk Dashboard Contest
A Four Part Event Series: AI + Observability: AI Agents, LLMs, Apps, & Infrastructure
